Fifty password reset requests produced fifty emails. CleanTalk limited the same sequence to five emails and 45 refusals. A later request delivered another email.
Limit WordPress Password Reset Email Spam with CleanTalk
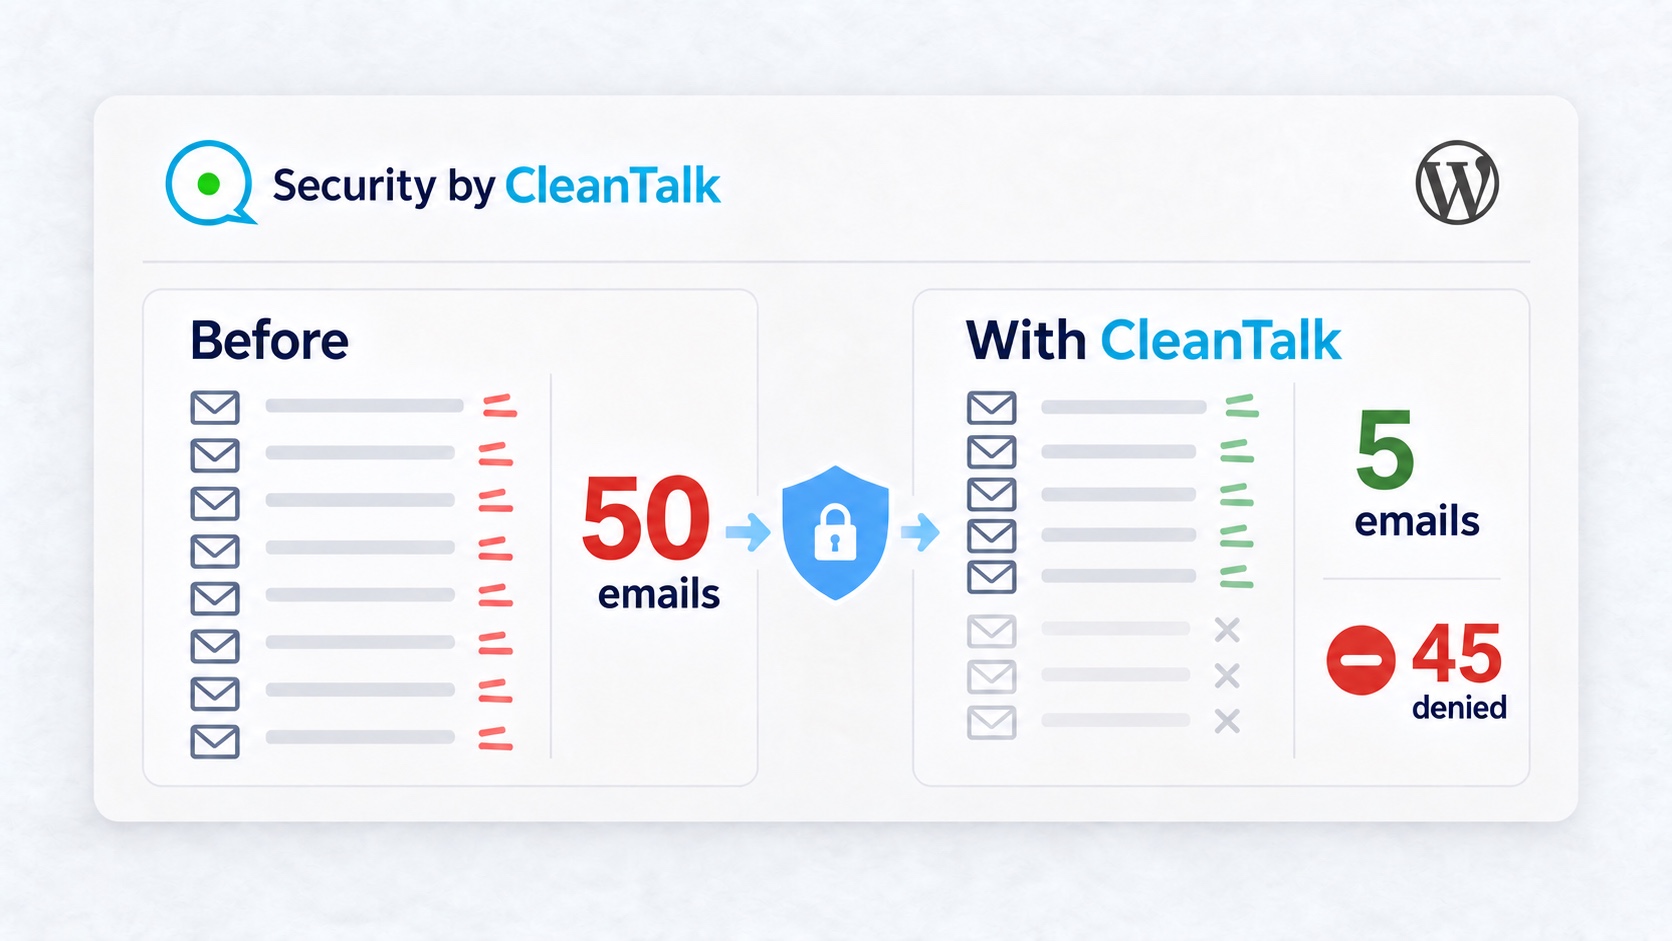
Fifty password reset requests produced fifty emails. CleanTalk limited the same sequence to five emails and 45 refusals. A later request delivered another email.
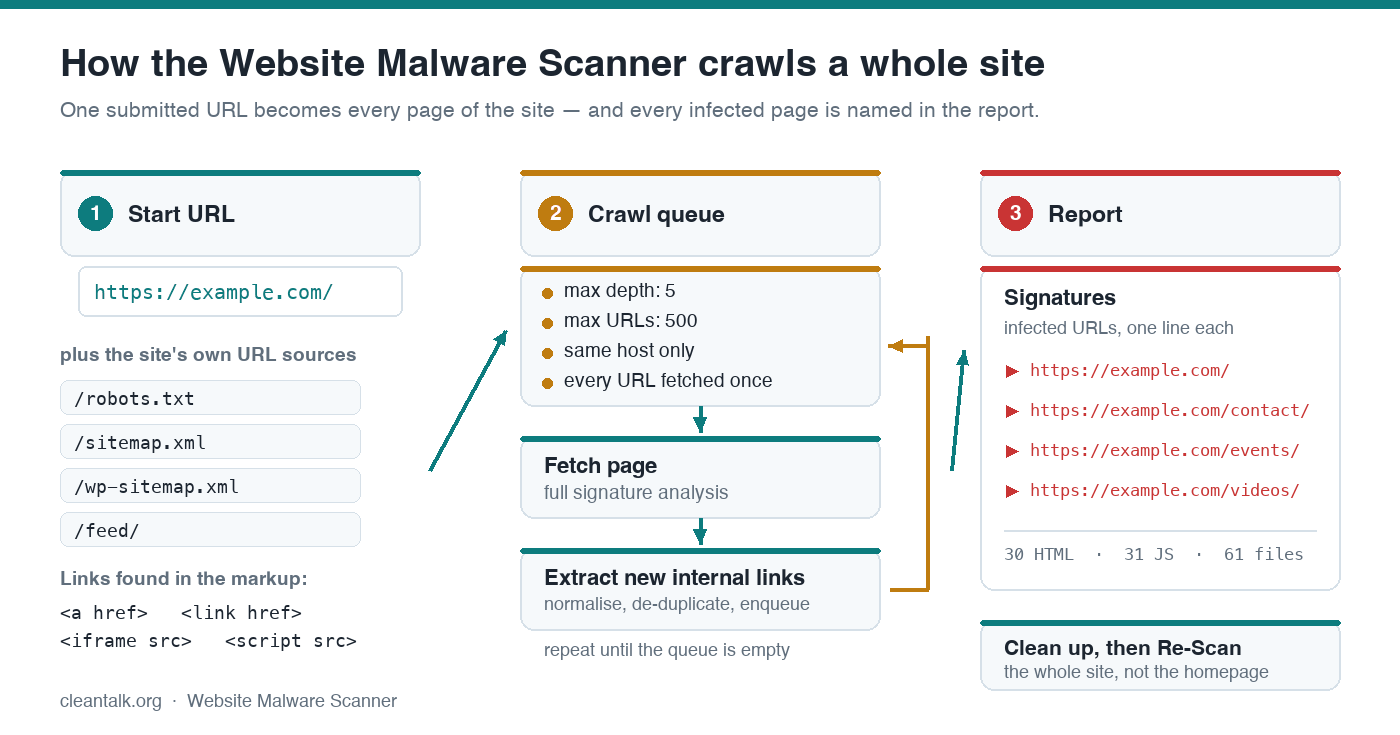
Malware often hides on inner pages while the homepage looks clean. The CleanTalk Website Malware Scanner now crawls the whole site – links, sitemaps, robots.txt and feeds – and lists every infected URL under Signatures.
CVE-2026-6459 is a Stored Cross-Site Scripting vulnerability in Essential Addons for Elementor Lite through version 6.6.2. An authenticated Author or higher-privileged user who can publish The Events Calendar events and assign a featured image can save a crafted event title. Opening that event in the EA Event Calendar popup with a Body Left or Body Right thumbnail executes an injected image load handler in the viewing browser, including an administrator’s session. The issue is fixed in version 6.6.3.
CVE-2026-11328 is a Stored Cross-Site Scripting vulnerability in Exclusive Addons for Elementor through version 2.7.9.8. A Contributor or higher-privileged user can save a crafted post title that is inserted into the Ex Duplicator link in the WordPress Posts list without attribute escaping. Moving the mouse over that link triggers the injected script in the viewing user’s browser. The issue is fixed in version 2.7.9.9.
CVE-2026-5821 affects Image Optimizer through version 1.7.4 and allows an authenticated Author to cause arbitrary file deletion through attachment backup metadata. The plugin trusts stored backup paths during attachment cleanup without checking that they belong to the expected image backups. Files writable by the web server may be removed, causing data loss, denial of service, or weakened site protection. The issue is fixed in version 1.7.5.
CVE-2026-104119: an Admin+ Stored XSS in the Simple Shopping Cart WordPress plugin (below 5.2.6), triggered through the PayPal API credentials settings. Details, timeline, impact on Multisite and remediation.
CVE-2026-11592 affects Email Subscribers & Newsletters, also known as Icegram Express, through version 5.9.27. A Contributor can open the hidden es_template editor, read the shared ig-es-admin-ajax-nonce from ig_es_js_data.security, and reuse it against AJAX handlers that do not enforce an effective capability check. The exposed workflow permits unauthorized mail setting changes, audience and campaign manipulation, contact imports, persistent workflows, and immediate email dispatch. The issue is fixed in version 5.9.28.
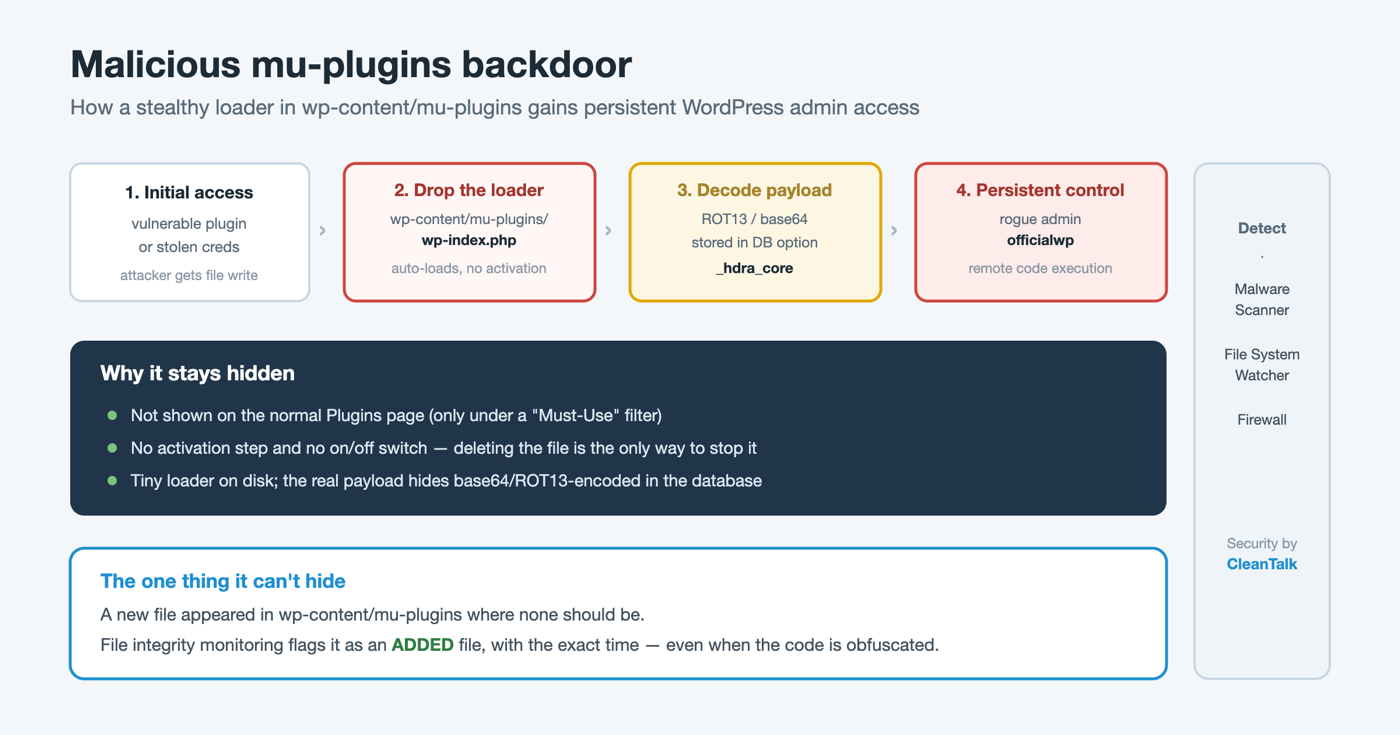
How the WordPress mu-plugins backdoor works: a hidden loader in wp-content/mu-plugins that auto-runs, stashes its payload in the database, and creates a rogue admin — plus indicators of compromise, detection and removal.
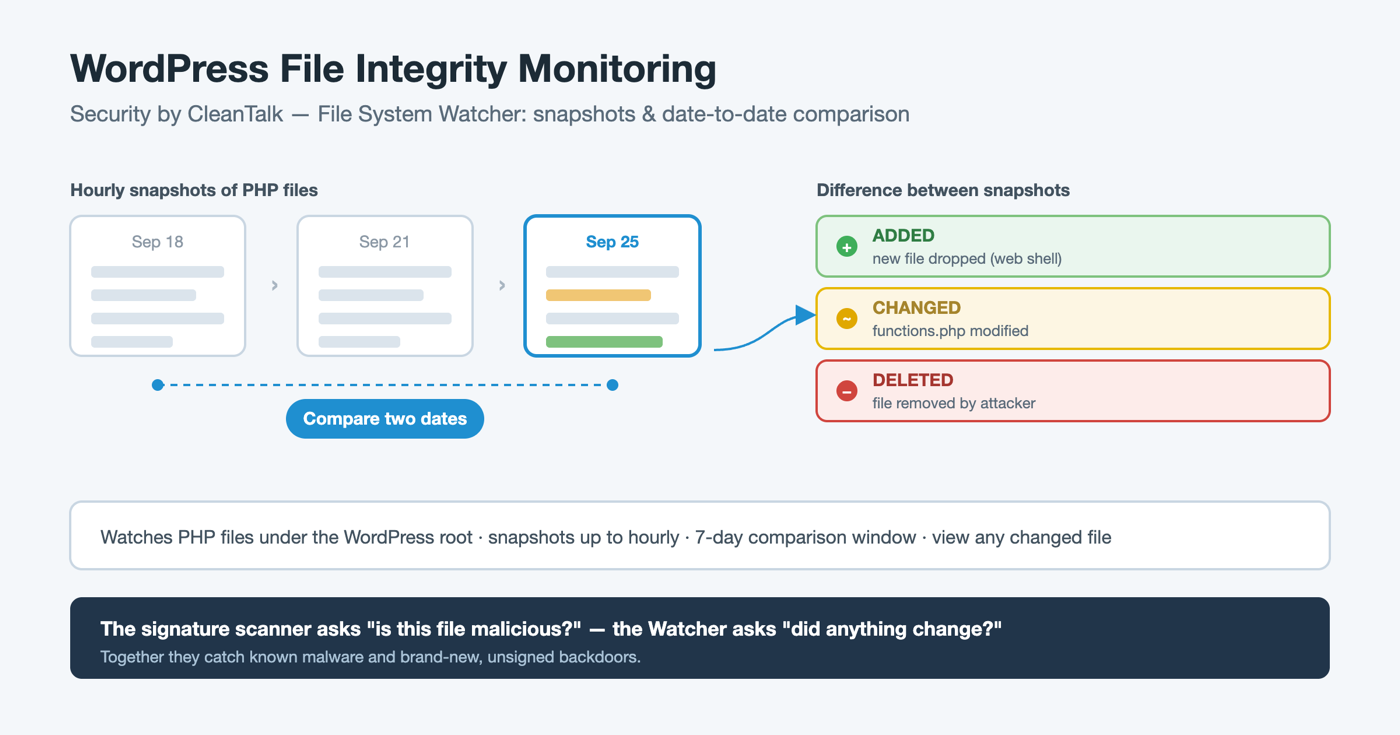
How the File System Watcher in Security by CleanTalk detects added, changed and deleted files on WordPress: hourly snapshots, date-to-date comparison, step-by-step setup, alternatives and FAQ.
Search submission plugins handle site URLs and service credentials while sending manual or automatic requests to external indexing endpoints. Instant Indexing for Google version 1.1.22 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65710. The review focused on settings permissions, credential handling, URL validation, manual and bulk submissions, automatic post events, remote API requests, response output, post type exclusions, and IndexNow controls.