Cron management plugins can inspect, create, pause, delete, and immediately execute scheduled tasks that affect many parts of a WordPress site. WP Crontrol version 1.21.2 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65702. The review focused on authorization for event management, request integrity, callback and argument display, custom schedules, URL validation, bulk actions, and exported event data.
Plugin Security Certification (PSC-2026-65701): “AMP” – Version 2.5.5

AMP integrations transform WordPress output, validate generated markup, and may direct visitors between standard and optimized page variants. AMP version 2.5.5 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65701. The review focused on administrative settings, markup sanitization, validation data, template processing, component handling, and safe page delivery.
Plugin Security Certification (PSC-2026-65700): “Converter for Media – Optimize images | Convert WebP & AVIF” – Version 6.6.5

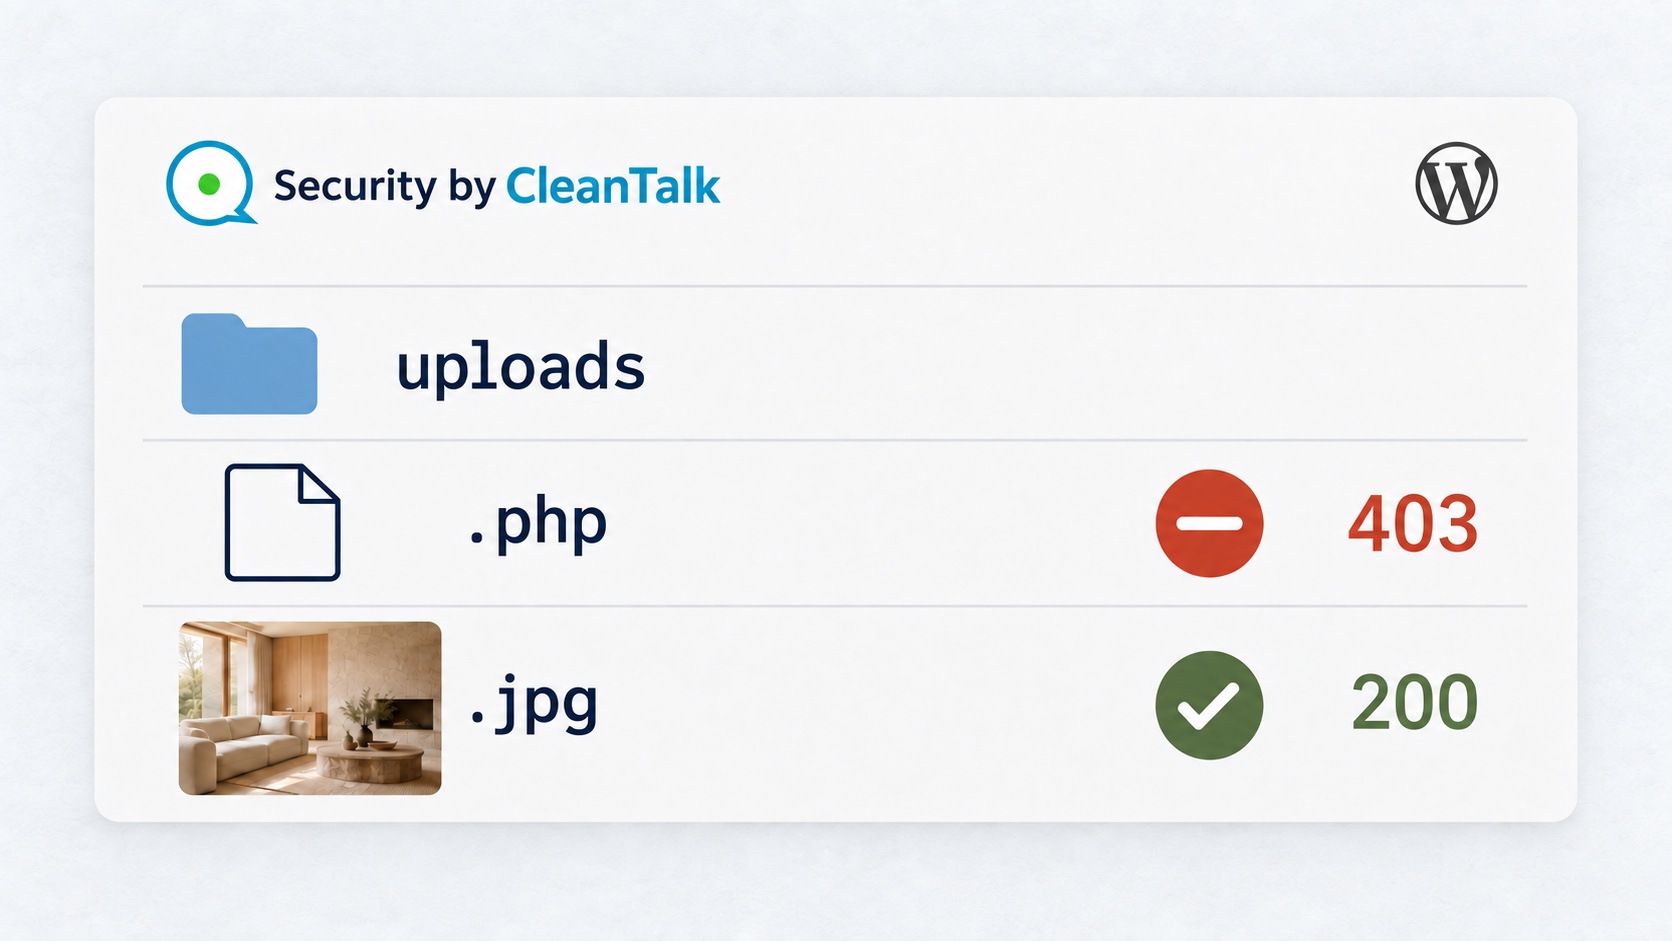
Image optimization plugins read files from the uploads directory, create alternative formats, and route visitor requests to generated assets. Converter for Media – Optimize images | Convert WebP & AVIF version 6.6.5 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65700. The review focused on source file validation, path confinement, conversion jobs, generated output, delivery rules, and permission checks around administrative actions.
Plugin Security Certification (PSC-2026-65697): “Child Theme Configurator” – Version 2.6.7

Child theme utilities inspect installed themes and can create or modify PHP, CSS, and configuration files inside the WordPress themes directory. Child Theme Configurator version 2.6.7 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65697. The review focused on administrative authorization, filesystem boundaries, theme and file selection, stylesheet parsing, template copying, and safe handling of configuration input.
Plugin Security Certification (PSC-2026-65696): “WP Mail Logging” – Version 1.16.0

Email logging plugins retain message bodies, recipient details, headers, attachments, and delivery errors that may contain sensitive operational data. WP Mail Logging version 1.16.0 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65696. The review focused on log access, stored message rendering, attachment references, search and bulk actions, resend requests, and protection of plugin settings.
Plugin Security Certification (PSC-2026-65695): “CookieAdmin – Cookie Consent Banner” – Version 1.2.3

Cookie consent tools combine public banner output with administrator-managed rules that determine when scripts and cookie groups can load. CookieAdmin – Cookie Consent Banner version 1.2.3 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-65695. The review focused on protected configuration, consent state processing, script identification rules, cookie scan data, and safe rendering of visitor choices.
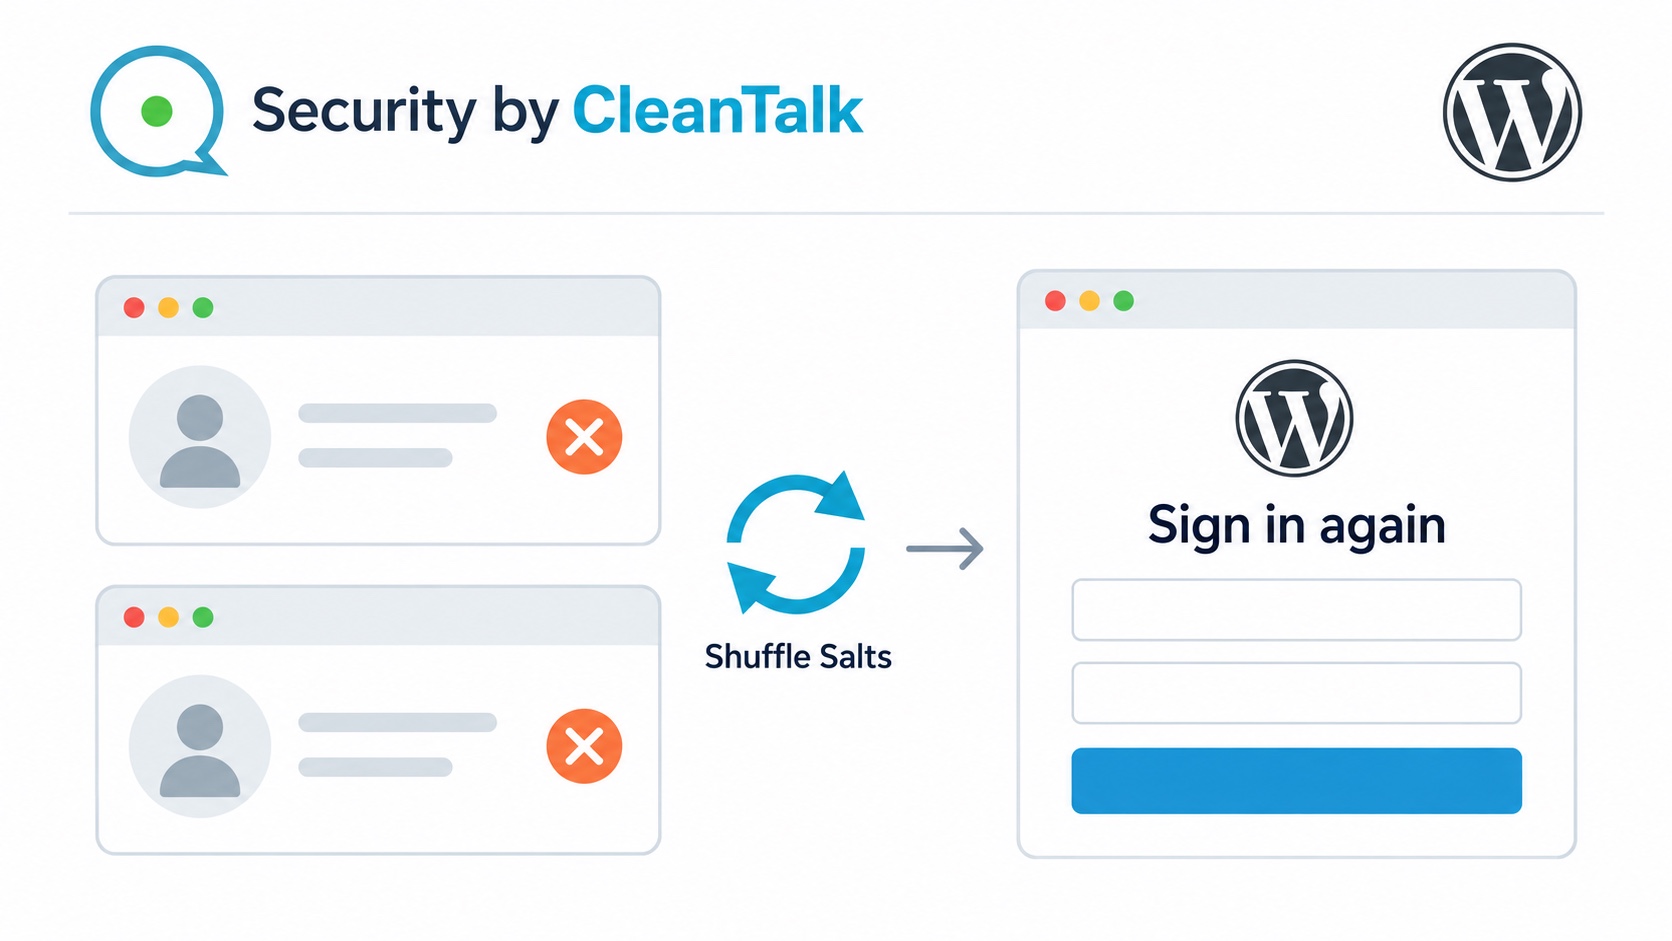
Force WordPress Users to Log Out with CleanTalk Shuffle Salts
CVE-2026-13245 – MaxButtons – Unauth Reflected XSS – POC

CVE-2026-13245 affects MaxButtons through version 9.8.5 and allows an unauthenticated attacker to inject an event handler into the admin list screen through the view query parameter. An administrator who opens a crafted URL and activates the injected access key can run JavaScript within their wp-admin session. This can expose administrative data or allow actions available to the victim account. The issue is fixed in version 9.8.6.
CVE-2025-15665 – BEAF – Admin+ Stored XSS – POC

CVE-2025-15665 affects the Ultimate Before After Image Slider & Gallery (BEAF) plugin and is an authenticated Admin+ Stored Cross-Site Scripting vulnerability in versions below 4.7.1. The BEAF Slider widget stores its Enter Shortcode value and passes it to do_shortcode() without escaping non-shortcode content, so an administrator or another trusted widget manager can persist markup that executes in the browser of any visitor who loads a page containing the widget. If an administrator views the affected page, the script runs in that authenticated origin and can become an account takeover path. The issue is fixed in version 4.7.1.