SPBCT Critical Updates separates known CVE matches from version-specific CleanTalk PSC records for installed WordPress plugins and themes.
SPBCT Critical Updates: Known CVEs and PSC Records
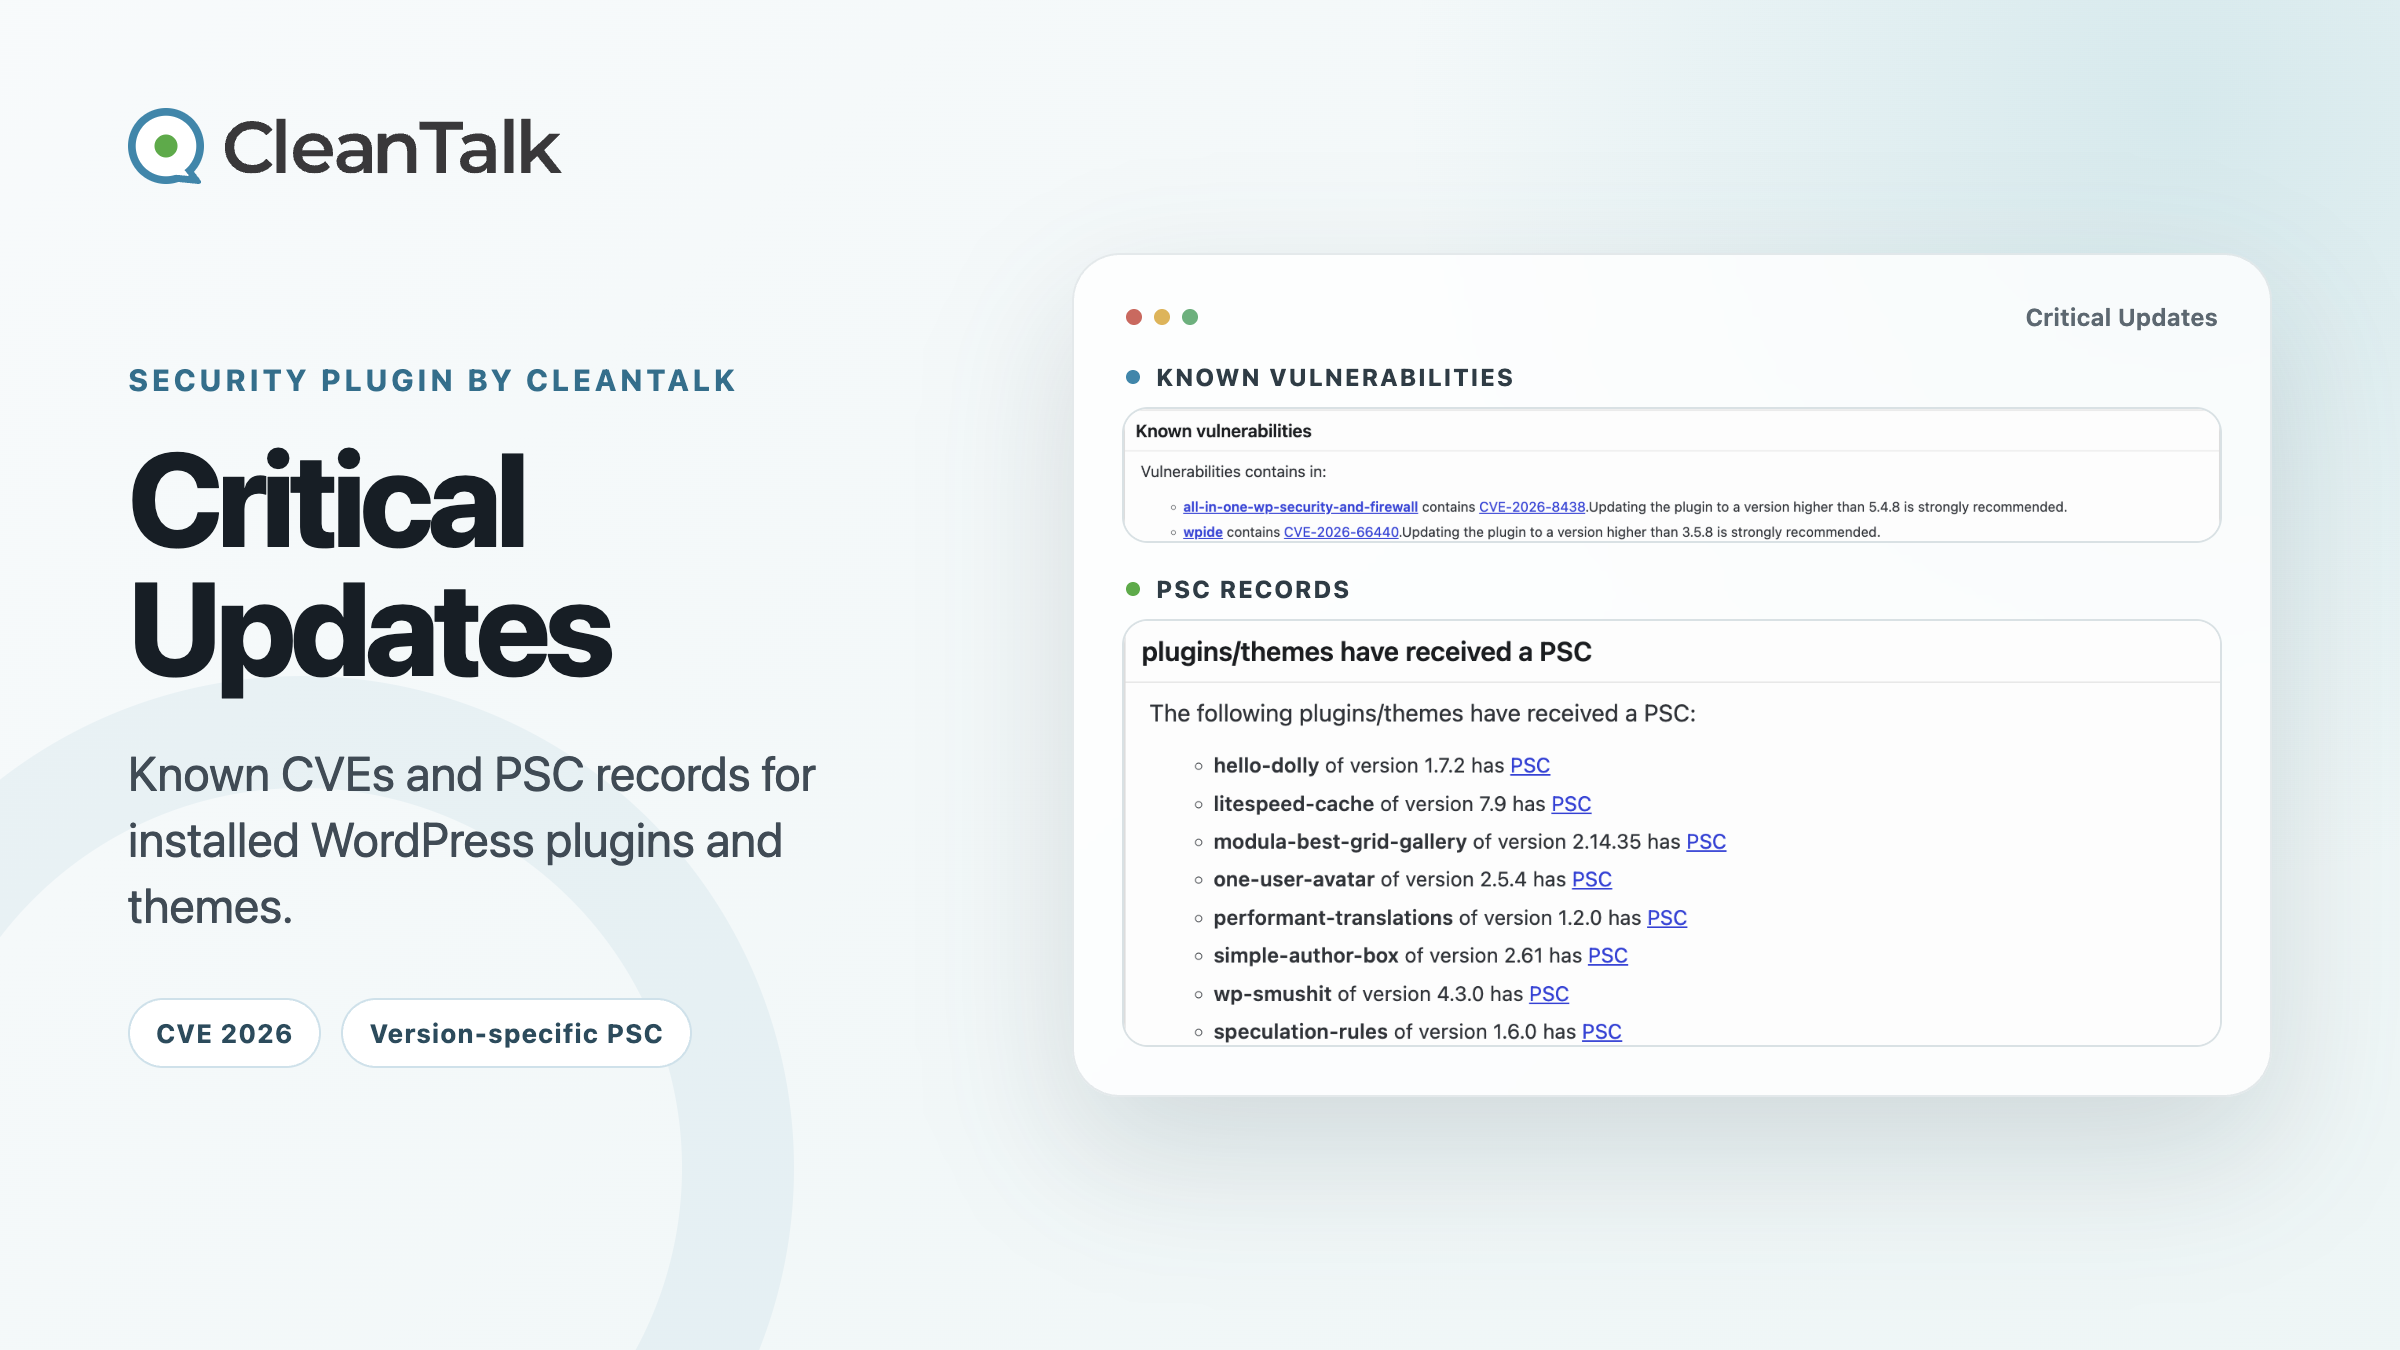
SPBCT Critical Updates separates known CVE matches from version-specific CleanTalk PSC records for installed WordPress plugins and themes.
CVE-2026-7526 affects PDF Embedder <= 4.9.3 and exposes site-wide plugin settings to authenticated Contributor+ users through the global pdfembPluginOptions JavaScript object. A saved premium license key can also be disclosed when the premium add-on is installed.
CVE-2026-3985 affects Creative Mail <= 1.6.9 with unauthenticated time-based SQL injection in the abandoned checkout flow. A crafted checkout UUID reaches an unprepared SQL query and can be used to infer sensitive database data.
CVE-2025-15345 affects MapGeo – Interactive Geo Maps and is an unauthenticated reflected Cross-Site Scripting vulnerability in versions up to and including 1.6.27. When a public page uses the display-map shortcode in demo mode, an attacker can supply an external JavaScript URL through the map parameter and make the victim browser load it under the vulnerable site context.
CVE-2026-6229 affects Royal Addons for Elementor and is an authenticated Contributor+ server-side request forgery vulnerability in the Data Table widget. In versions through 1.7.1057, a user-controlled CSV URL can bypass the Google Sheets substring check, reach arbitrary internal or external HTTP services, and expose response data after it is parsed into the rendered table.
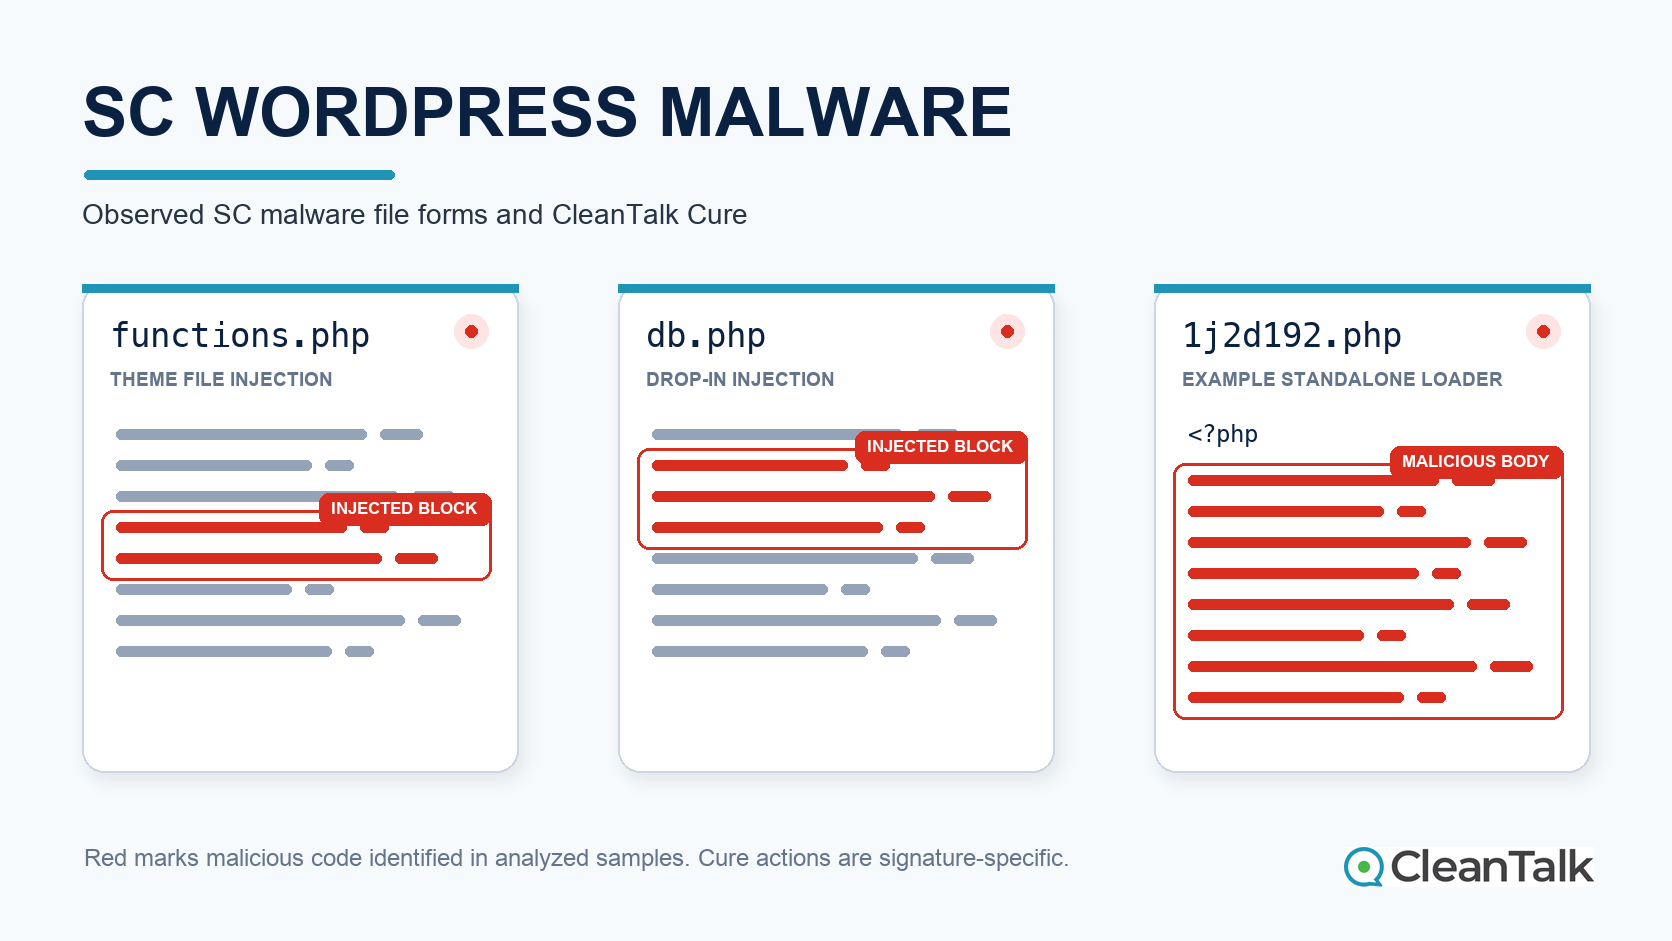
See how SC WordPress malware infects functions.php, db.php, and randomly named PHP loaders, and how CleanTalk detects and safely cures verified matches.
CVE-2025-11762 affects HubSpot All-In-One Marketing and exposes installed plugin names and versions to authenticated Contributor+ users through the global leadinConfig JavaScript object.
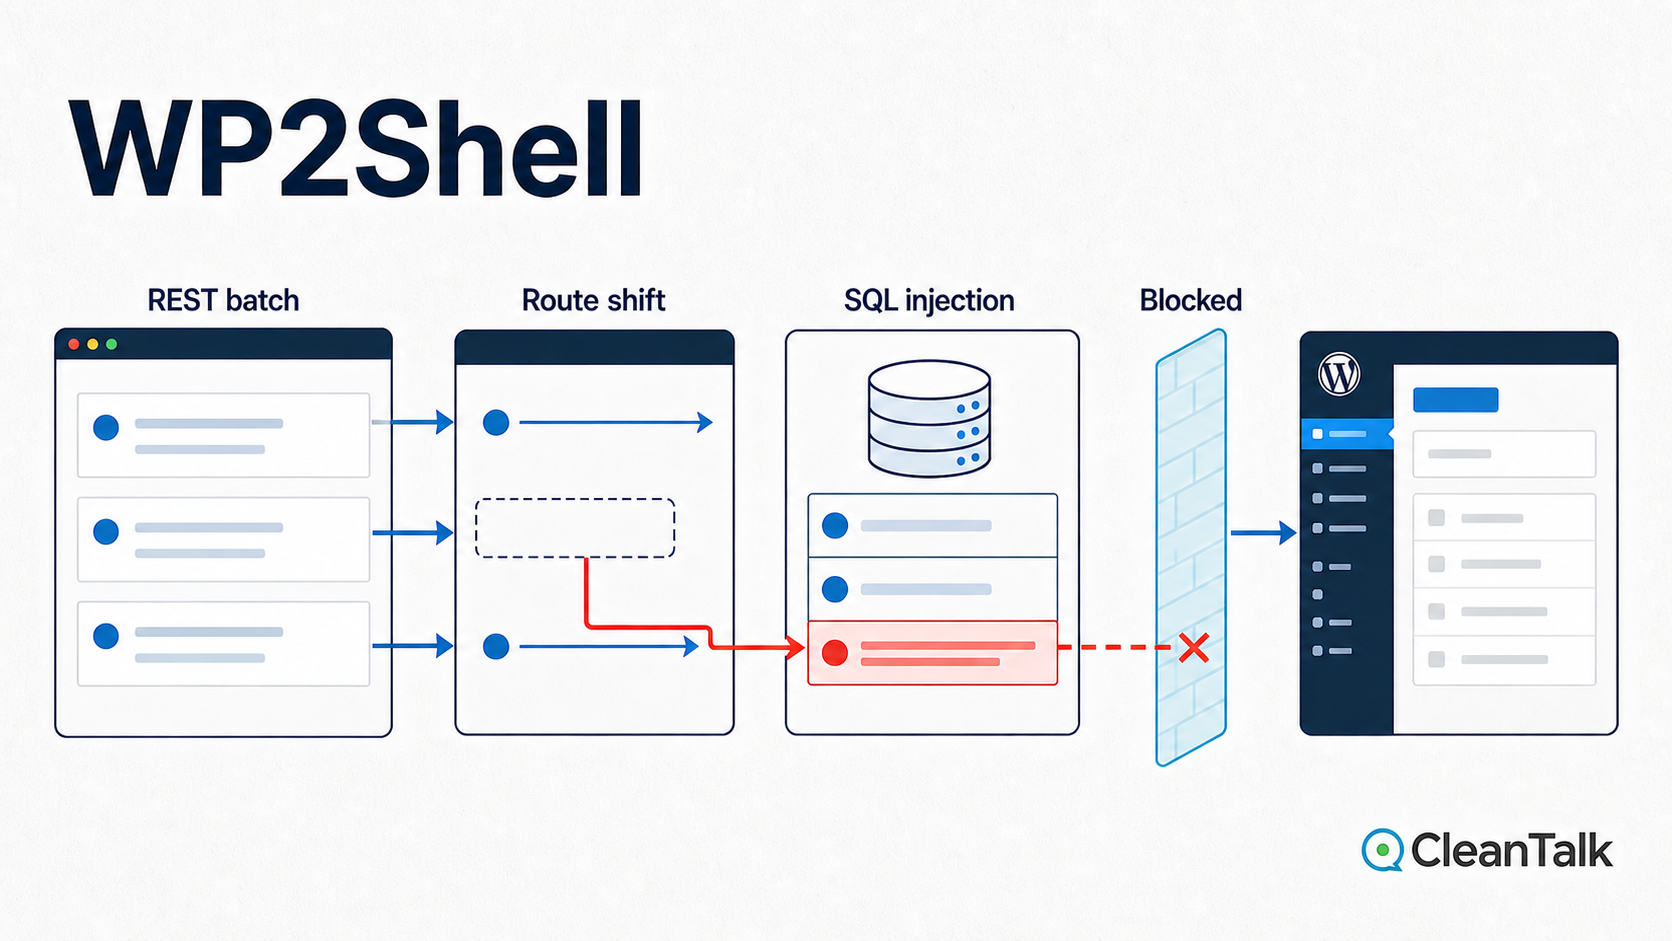
WP2Shell is an actively exploited WordPress core RCE chain. See affected versions, code-level CVE analysis, IOCs, fixes, and CleanTalk protection.
Contact Form 7 extensions can influence spam checks, stored submissions, redirects, and outbound webhooks. These features cross the boundary between anonymous form input, privileged records, external destinations, and front-end responses. CF7 Apps – Honeypot, Database, Redirection, Webhook, and Addons for Contact Form 7 version 3.6.1 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-64684, confirming that the plugin was reviewed from a secure code perspective with attention to public submissions, anti-spam checks, stored records, redirect targets, webhook configuration, and administrator access.
Content ordering plugins turn drag-and-drop administrator actions into persistent changes across posts, pages, taxonomies, and sites. Those updates must be limited to authorized objects and protected from forged requests. Intuitive Custom Post Order version 3.2.0 has successfully completed the CleanTalk Plugin Security Certification process and received PSC-2026-64683, confirming that the plugin was reviewed from a secure code perspective with attention to reorder permissions, request integrity, object identifiers, taxonomy operations, multisite scope, and stored ordering data.