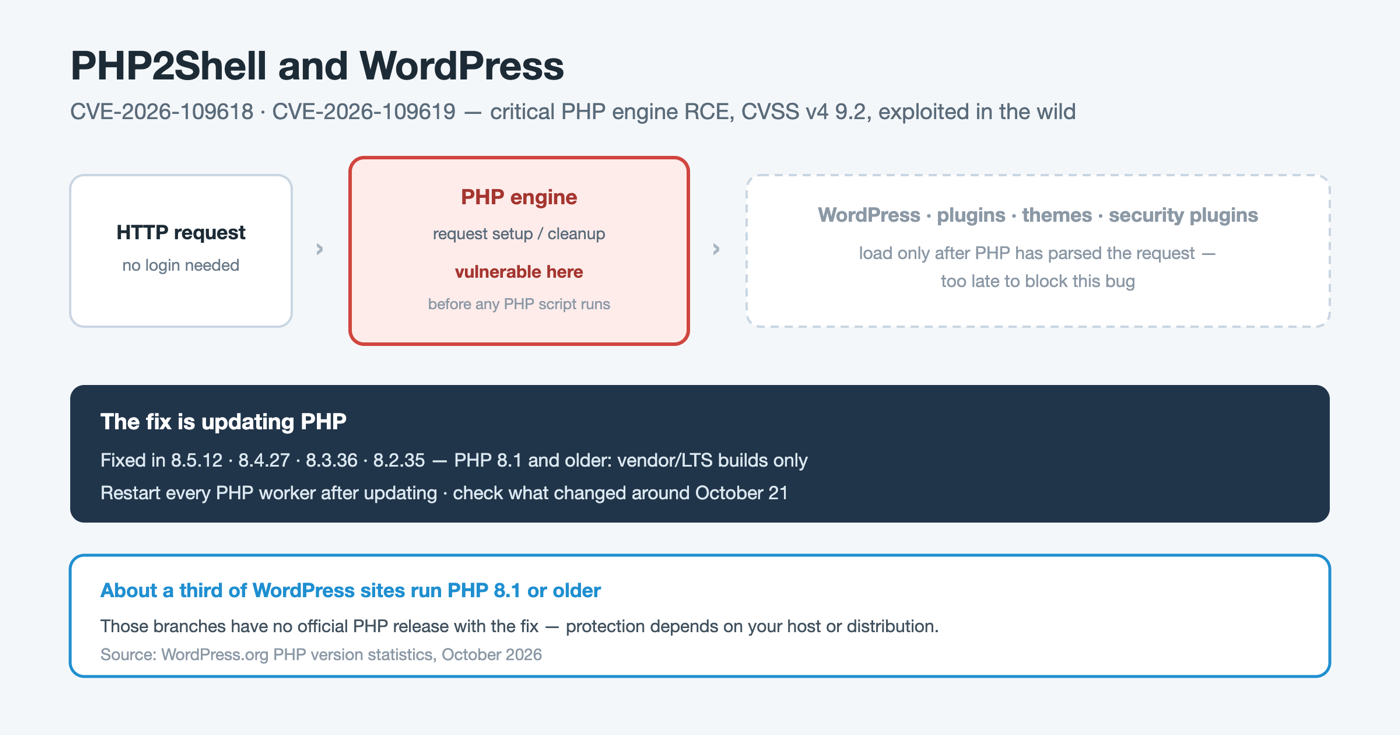
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is a critical, exploited RCE in the PHP engine. How critical it is for WordPress sites, who is exposed, how to check your PHP version, and what to do.
CVE-2025-15703 – WP Job Openings – Admin+ Stored XSS – POC
CVE-2026-13116 - PDF Invoices & Packing Slips for WooCommerce - IDOR - POC

CVE-2026-13116 is an insecure direct object reference in PDF Invoices & Packing Slips for WooCommerce through version 5.14.0. When Full document-link access is enabled, missing order-level authorization can allow a low-privileged content author to obtain a public link to another customer’s invoice or packing slip. Exposed documents may contain customer contact information, addresses, purchased items, totals and order notes. The supplied research describes version 5.9.2, while the public advisory identifies 5.15.0 as the first fixed release.
CVE-2026-6459 - Essential Addons for Elementor - Stored XSS - POC

CVE-2026-6459 is a Stored Cross-Site Scripting vulnerability in Essential Addons for Elementor Lite through version 6.6.2. An authenticated Author or higher-privileged user who can publish The Events Calendar events and assign a featured image can save a crafted event title. Opening that event in the EA Event Calendar popup with a Body Left or Body Right thumbnail executes an injected image load handler in the viewing browser, including an administrator’s session. The issue is fixed in version 6.6.3.
CVE-2026-11328 – Exclusive Addons for Elementor – Stored XSS – POC

CVE-2026-11328 is a Stored Cross-Site Scripting vulnerability in Exclusive Addons for Elementor through version 2.7.9.8. A Contributor or higher-privileged user can save a crafted post title that is inserted into the Ex Duplicator link in the WordPress Posts list without attribute escaping. Moving the mouse over that link triggers the injected script in the viewing user’s browser. The issue is fixed in version 2.7.9.9.
CVE-2026-5821 – Image Optimizer – Author+ File Deletion – POC

CVE-2026-5821 affects Image Optimizer through version 1.7.4 and allows an authenticated Author to cause arbitrary file deletion through attachment backup metadata. The plugin trusts stored backup paths during attachment cleanup without checking that they belong to the expected image backups. Files writable by the web server may be removed, causing data loss, denial of service, or weakened site protection. The issue is fixed in version 1.7.5.
CVE-2026-104119 – Simple Shopping Cart – Admin+ Stored XSS via PayPal API Credentials – PoC
CVE-2026-11592 – Icegram Express – Missing Authorization – POC

CVE-2026-11592 affects Email Subscribers & Newsletters, also known as Icegram Express, through version 5.9.27. A Contributor can open the hidden es_template editor, read the shared ig-es-admin-ajax-nonce from ig_es_js_data.security, and reuse it against AJAX handlers that do not enforce an effective capability check. The exposed workflow permits unauthorized mail setting changes, audience and campaign manipulation, contact imports, persistent workflows, and immediate email dispatch. The issue is fixed in version 5.9.28.
CVE-2026-10096 – Qi Blocks – Author+ IDOR – POC

CVE-2026-10096 affects Qi Blocks through version 1.4.9 and allows authenticated Author+ users to overwrite stored styles for posts they cannot edit through the qi-blocks/v1/update-styles REST route. The endpoint trusts the supplied page_id after checking only edit_posts and publish_posts, so a user can target another author’s post. Reserved template and widget values broaden the impact to shared site surfaces, enabling persistent frontend defacement, hidden content, and degraded page usability. The issue is fixed in version 1.5.0.
CVE-2026-13245 – MaxButtons – Unauth Reflected XSS – POC

CVE-2026-13245 affects MaxButtons through version 9.8.5 and allows an unauthenticated attacker to inject an event handler into the admin list screen through the view query parameter. An administrator who opens a crafted URL and activates the injected access key can run JavaScript within their wp-admin session. This can expose administrative data or allow actions available to the victim account. The issue is fixed in version 9.8.6.